01
Assess Your Security Posture
Review security assessment data, findings, and overall exposure.
Compliance
Understand where you stand against key cybersecurity regulations and standards with clear, actionable compliance reporting.
How It Works
A structured assessment process turns security data and findings
into clear priorities, reports, and actionable next steps.
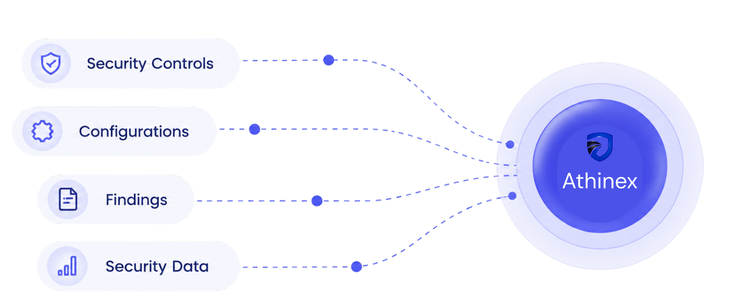
Review security assessment data, findings, and overall exposure.
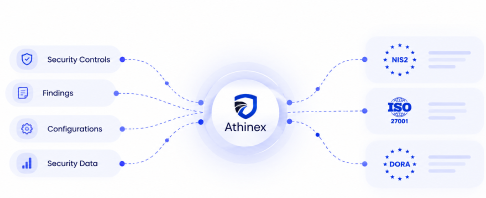
Connect controls and findings to the requirements of applicable regulations and standards.
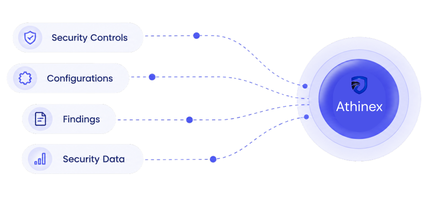
Highlight requirements that are compliant, partially addressed, or require attention.
Transform assessment results into clear, structured reports for stakeholders and compliance teams.
Prioritize remediation and continuously improve compliance readiness.
Security Reporting
Security reports provide a structured view of identified findings,
helping teams understand severity, track status, and focus
remediation efforts.
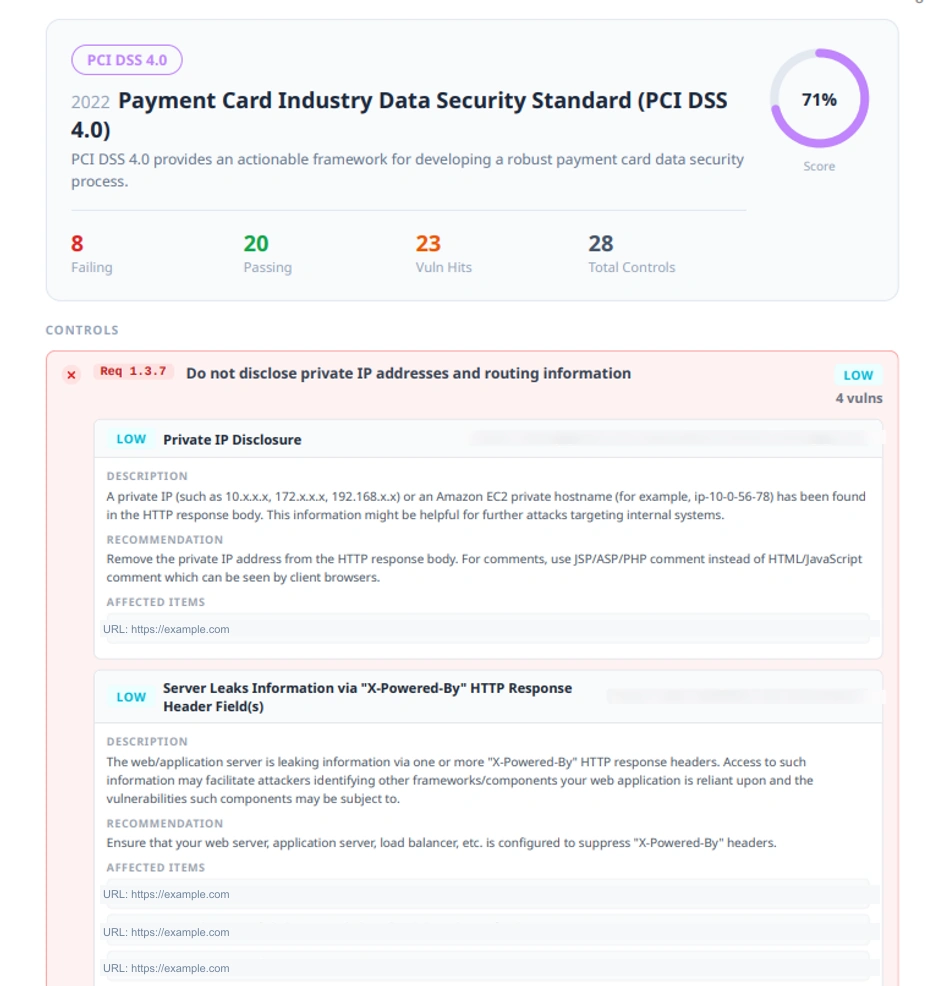
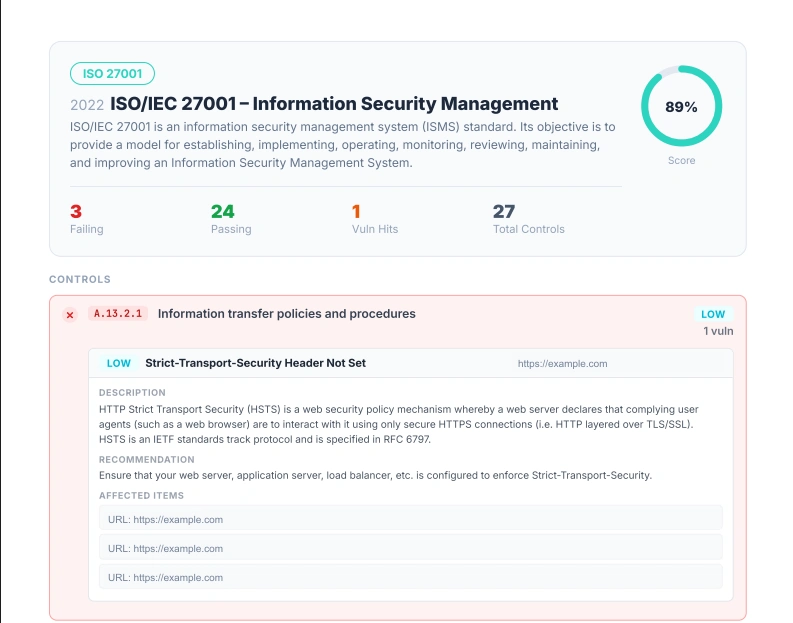
Review PCI DSS 4.0 control findings, severity, and affected items in one structured security report.
Understand your current level of security exposure.
See identified findings across your security assessments.
Distinguish critical, high, medium, and lower-severity findings.
Understand which security issues require attention first.
Athinex helps security teams continuously discover exposure,
understand real risk, and orchestrate remediation across the entire attack surface.